Discovering your website has been defaced, blacklisted by Google, or infected with malicious redirects stops business immediately. Lingering backdoors, infected core files, and compromised database tables leave your customer data exposed and kill your search rankings. We remove active malware, eliminate hidden backdoors, lift search engine blacklists, and harden your entire server setup so your site stays safe permanently.
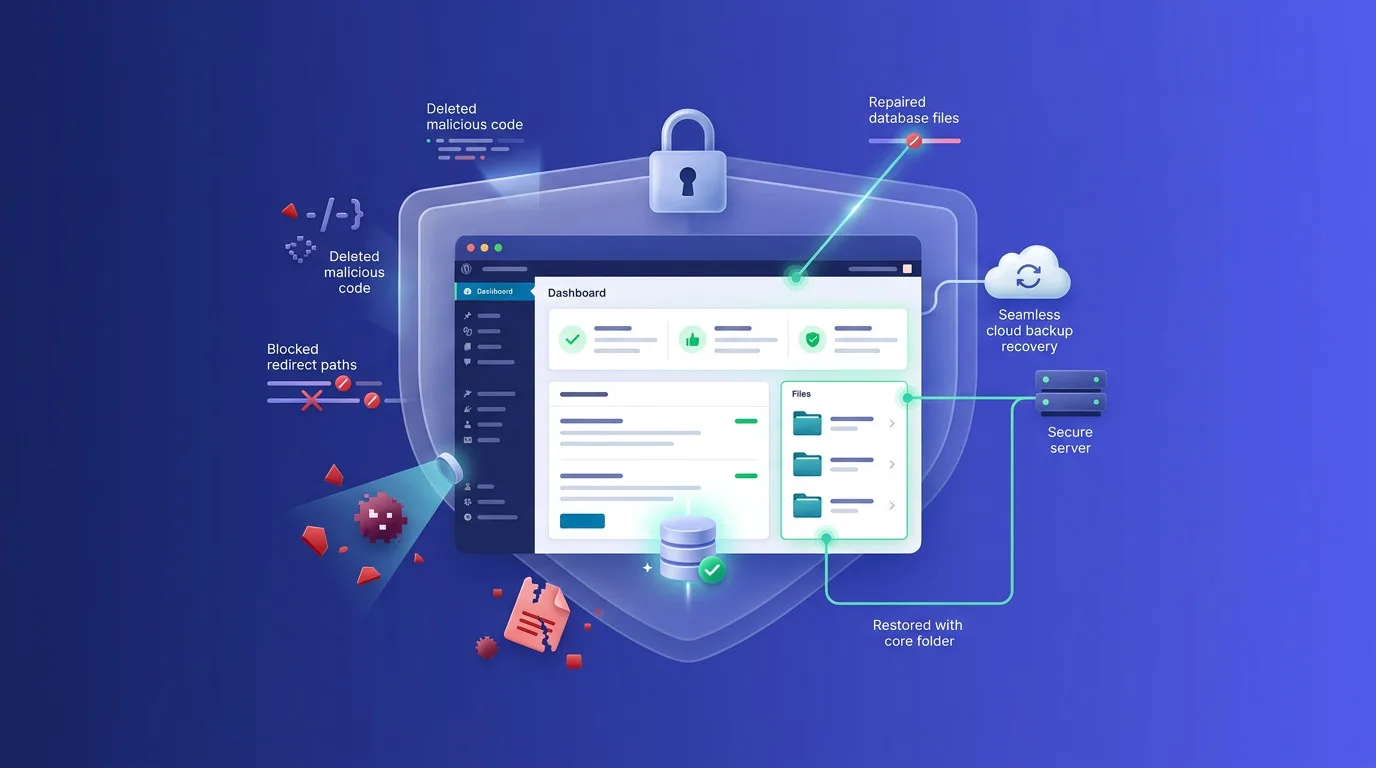
We locate and strip out malicious PHP scripts, hidden database injections, and malicious redirect links across your site.
We clean flagged files and submit formal review requests to Google and security vendors to restore your search traffic.
We track down rogue admin accounts, hidden cron triggers, and disguised files that attackers use to regain access.
We set up Web Application Firewalls, disable file execution in upload folders, and enforce strict security headers.
Automatic security plugins often delete infected files without fixing the underlying vulnerability, causing malware to return within days. Attackers hide malicious code inside deep database rows, fake image formats, and cloned core folders. We conduct a thorough manual and deep-file forensic audit. We sanitize your database, replace modified core and plugin files with clean source copies, and close the initial entry point so attacks cannot repeat.
Do not wait for a red security warning screen to find out attackers targeted your website. We set up real-time firewall monitoring tools that track blocked brute-force attempts, unauthorized file change alerts, and malicious IP bans right from your dashboard. You get full visibility into your site defenses, keeping your web presence secure every hour.
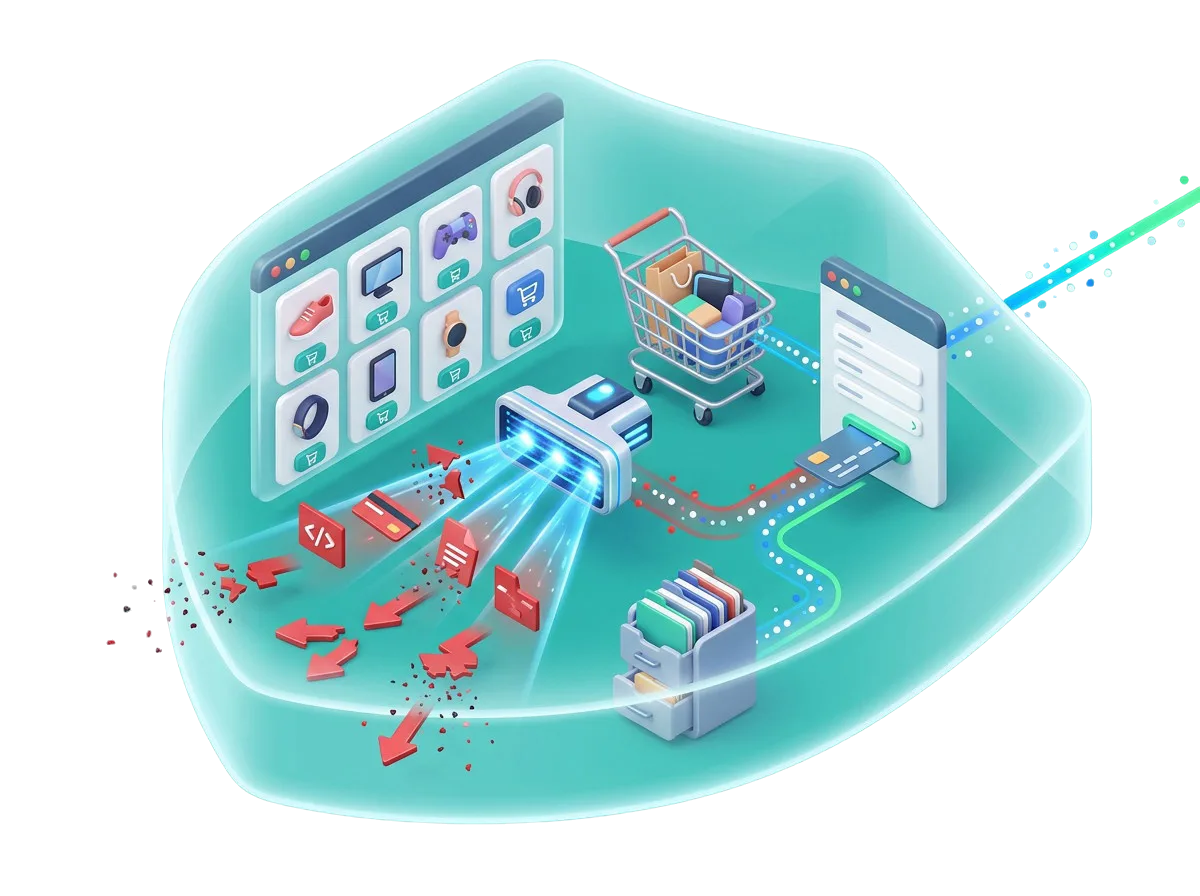
Protect your checkout and payment data from credit card skimmers. We remove malicious injection scripts and secure customer checkout paths so buyers can shop without data risk.
When a client website gets hacked or flagged by web hosts, let our specialists step in. We clean the file system, resolve host suspensions, and harden site defenses to protect client trust.
Protect your new brand from automated vulnerability scanners. We audit file permissions, lock down database prefixes, and configure firewalls before launch so your site resists attacks.
Google Ads suspends accounts immediately when landing pages contain malware redirects. We eliminate the malicious scripts and clear malware flags so your ad accounts get approved again.
$ 49.00
$ 99.00
$ 199.00
$ 490.00
$ 990.00
$ 1990.00
Project Step 1
“We inspect your website core files, themes, plugins, uploads folder, and database tables against clean official checksums. We identify all injected scripts, modified core files, and active redirects.”
Project Step 2
“We outline an isolation plan to block active malicious traffic, isolate the entry point, and structure file restoration. You receive a clear scope of work before file modifications begin.”
Project Step 3
“If temporary maintenance is required during file sanitization, we deploy a clean, branded maintenance screen so visitors know your business is handling scheduled technical upkeep.”
Project Step 4
“We replace compromised core files, clean infected database entries, revoke compromised API keys and passwords, block script execution in uploads, and configure firewall rules.”
Project Step 5
“We run secondary deep scans across all directories to ensure zero malicious traces remain. We submit review requests to Google Safe Browsing and security blacklists to restore site reputation.”
Project Step 6
“We apply real-time firewall shields, verify live traffic, and restore normal operations. You receive a full incident post-mortem detailing how entry occurred, what was fixed, and security guidelines.”
Share your website details with us to get a complete security forensic audit, cleanup plan, and clear quote.